dilneiss/laravel-password-exposed-validation-rule
Laravel validation rule that checks if a password has been exposed in a data breach
1,094
| Install | |
|---|---|
composer require dilneiss/laravel-password-exposed-validation-rule |
|
| Latest Version: | 3.1 |
| PHP: | ^7.1||^8.0||8.1||8.2 |
| Laravel: | 5 – 11 |
| License: | LGPL-3.0-only |
| Last Updated: | May 29, 2024 |
| Links: | GitHub · Packagist |
Maintainer: dilneiss
🔒 Laravel Password Exposed Validation Rule
This package provides a Laravel validation rule that checks if a password has been exposed in a data breach. It uses the haveibeenpwned.com passwords API via the divineomega/password_exposed library.


Installation
To install, just run the following Composer command.
composer require divineomega/laravel-password-exposed-validation-rule
Please note that this package requires Laravel 5.1 or above.
Usage
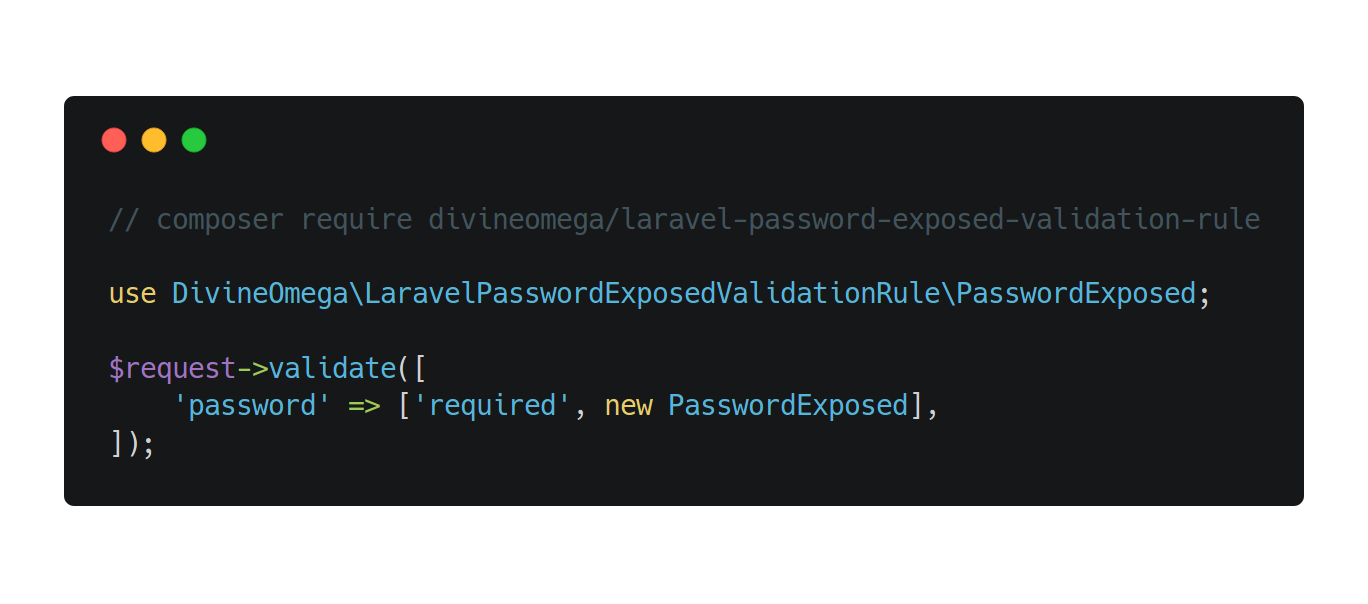
The following code snippet shows an example of how to use the password exposed validation rule.
use DivineOmega\LaravelPasswordExposedValidationRule\PasswordExposed;

$request->validate([
    'password' => ['required', new PasswordExposed()],
]);
If you wish, you can also set a custom validation message, as shown below.
use DivineOmega\LaravelPasswordExposedValidationRule\PasswordExposed;

$request->validate([
    'password' => ['required', (new PasswordExposed())->setMessage('This password is not secure.')],
]);
Related Packages
doctrine/dbal
Powerful PHP database abstraction layer (DBAL) with many features for database s...
648,266,899
9,701
laravel/serializable-closure
Laravel Serializable Closure provides an easy and secure way to serialize closur...
429,221,767
607
nunomaduro/collision
Cli error handling for console/command-line PHP applications.
403,217,078
4,664
Version History
| Version | Released | PHP | Laravel | License |
|---|---|---|---|---|
| 3.1 | ^7.1|| | ^5.1|| | LGPL-3.0-only | |
| 3.0 | ^7.1|| | ^5.1|| | LGPL-3.0-only |